Project Risks
How to assess project risks, estimate potential losses and spot trouble before it’s too late. Risk registers, probability–impact matrices and EMV.
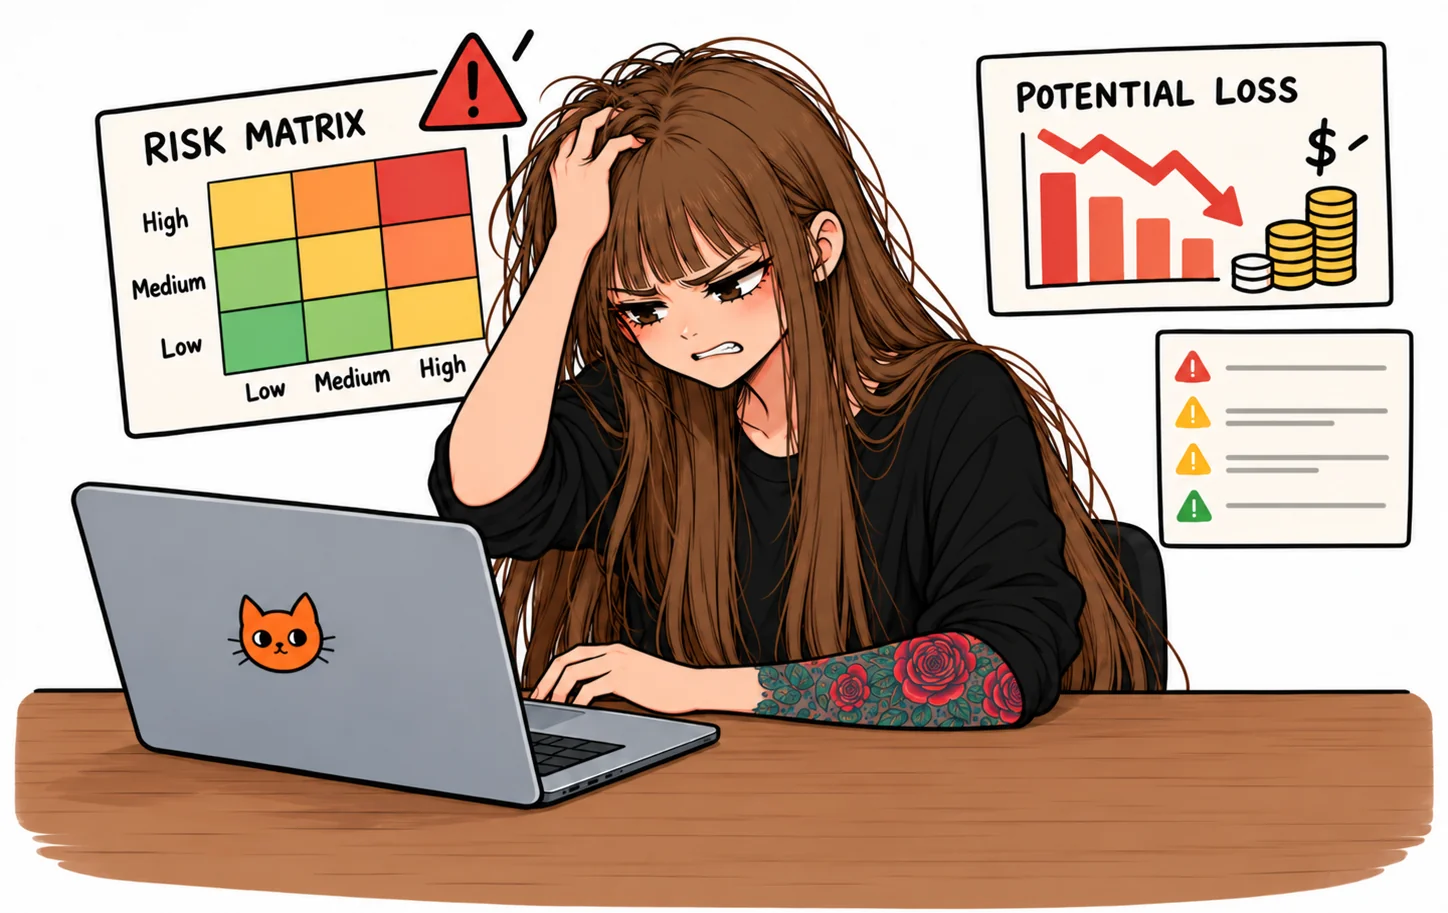
We’re on track
We've already covered project economics, so let's use the same example of a company developing a client portal. The budget is 1 million rubles, and the timeline is four months. The team is working, but there's still no access to the partner's API, some requirements haven't been agreed on, and the client hasn't appointed anyone responsible for acceptance testing. Access is already delayed, and development has stalled. We're assuming the API matches its documentation, but nobody has actually checked. And we've already based the project estimate on that assumption.
Where to look for risks
Requirements, technical dependencies, the team, the budget, approvals. Walk through the plan with your colleagues and check which assumptions are holding the whole thing together. To assess the risks, we use a probability–impact matrix. Score each factor from 1 to 5, then multiply the two scores.
| Risk | Probability | Impact | Score |
|---|---|---|---|
| Delayed API access | 4 | 5 | 20 |
| Requirements changes | 3 | 4 | 12 |
| Developer unavailable | 2 | 4 | 8 |
| Delayed acceptance | 4 | 3 | 12 |
The higher the score, the more attention the risk deserves. Agree on the scale first, though, or everyone will assess the consequences differently. Multiplying two subjective scores doesn’t magically turn them into an accurate forecast. The results go into the risk register: description, assessment, owner, trigger, response actions and status. Without the last three fields, it’s just a list of things that might go wrong.
What could the risk cost us?
EMV (Expected Monetary Value) lets us estimate the expected financial loss.
Suppose there’s a 30% chance the integration will need extra work, with a potential cost of RUB 200,000.
0.3 × 200,000 = RUB 60,000.
That’s an expected value, not an invoice. If the risk materialises, we could spend the full RUB 200,000. If it doesn’t, we spend nothing.
| Risk | Probability | Potential loss | EMV |
|---|---|---|---|
| Extra integration work | 30% | RUB 200,000 | RUB 60,000 |
| UI rework | 20% | RUB 100,000 | RUB 20,000 |
| Additional testing | 25% | RUB 80,000 | RUB 20,000 |
| Total | RUB 100,000 |
That gives us RUB 100,000 in expected losses. It’s a useful starting point for discussing a contingency reserve, but the total EMV guarantees nothing, especially if several risks hit at once. It also helps to know where those percentages came from.
What to do about the risks
For threats, four response strategies are to avoid, mitigate, transfer or accept the risk. Request test access early, check the documentation and prepare mocks. If access hasn’t arrived by the agreed date, bring in the owners and review the plan. Better to agree on the response before the integration blocks development.
| Risk | Owner | Trigger | Response |
|---|---|---|---|
| Delayed API access | PM, tech lead | No access by the checkpoint date | Escalate, use mocks, revise the plan |
| Requirements changes | PM, analyst | New scope after sign-off | Assess the impact, agree on changes |
| Delayed acceptance | PM, client | No feedback by the deadline | Escalate, update the schedule |
It’s in the register
Update the register when requirements, deadlines or dependencies change. Once a risk materialises, log it as an issue, record the actions and reassess the impact. A spreadsheet will do for a small project. Larger projects need reserves and ongoing monitoring.
If the integration falls through after the PM has spent a month reporting that it might, everyone has technically been warned. A fat lot of good that does now.
I’m a project manager. About working with russian clients and teams, sharing experience and things I’ve noticed.
The content published on this website is intended for informational and analytical purposes and reflects the author's professional experience, personal opinions, and subjective assessments. Any recommendations provided are not universal guidelines and may need to be adapted to specific circumstances, agreements, and workflows. Discussions of professional practices, products, and management decisions are intended to evaluate their effectiveness, not to damage anyone's honor, dignity, or reputation. Examples may be fictional, generalized, or anonymized and are not intended to disclose confidential information.